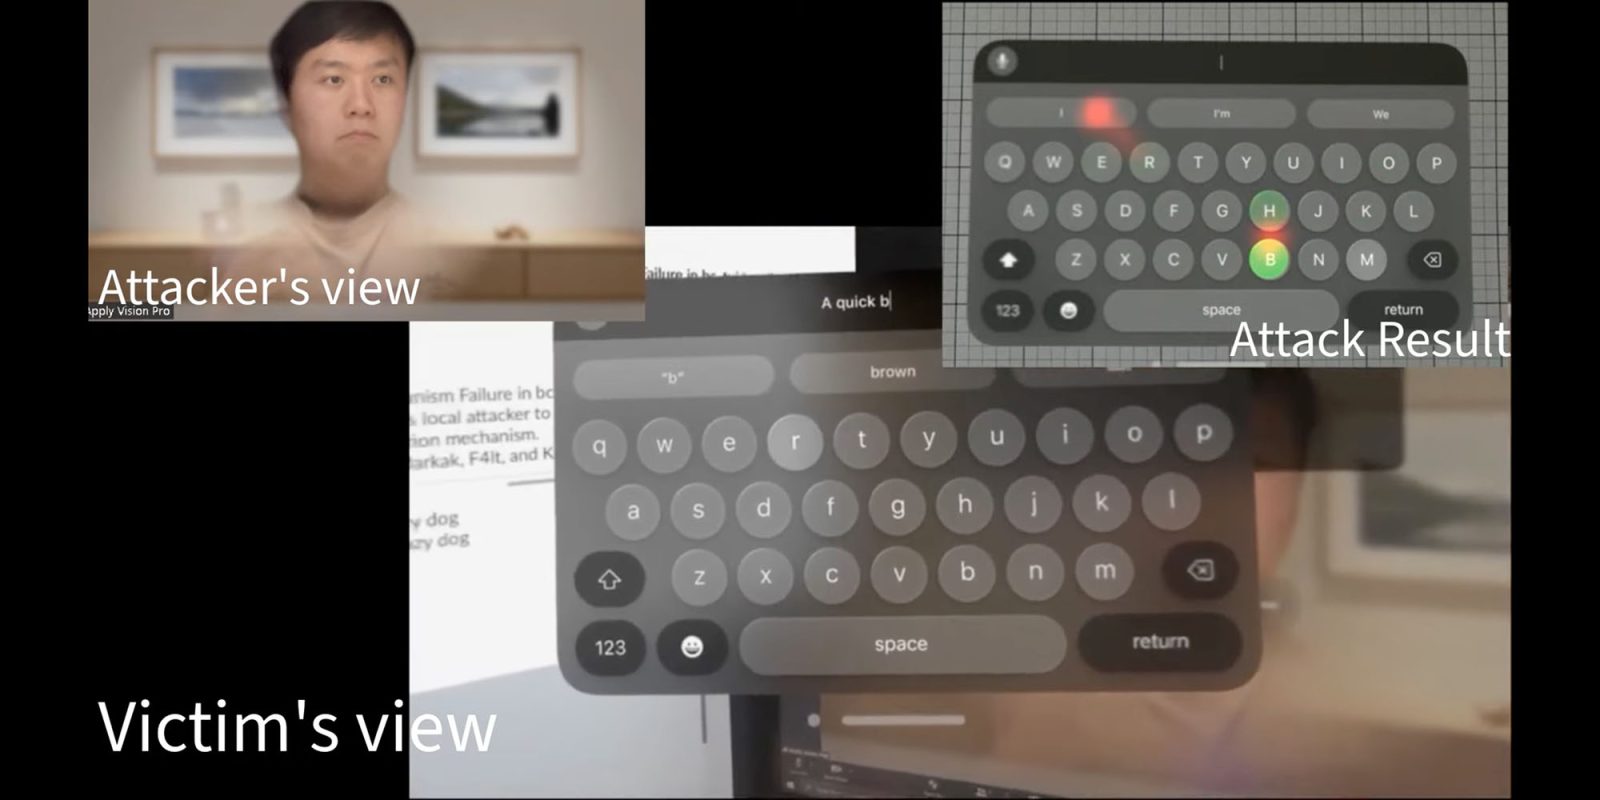
Security researchers came up with a pretty wild Vision Pro exploit. Dubbed GAZEploit, it’s a method of working out the passwords of Vision Pro users by watching the eye movements of their avatars during video calls.
They’ve put together a YouTube video (below) to demonstrate how tracking the avatar’s eye movements accurately detects the virtual keys the Vision Pro user is looking at when typing …
9to5Mac Security Bite is exclusively brought to you by Mosyle, the only Apple Unified Platform.Making Apple devices work-ready and enterprise-safe is all we do. Our unique integrated approach to management and security combines state-of-the-art Apple-specific security solutions for fully automated Hardening & Compliance, Next Generation EDR, AI-powered Zero Trust, and exclusive Privilege Management with the most powerful and modern Apple MDM on the market. The result is a totally automated Apple Unified Platform currently trusted by over 45,000 organizations to make millions of Apple devices work-ready with no effort and at an affordable cost. Request your EXTENDED TRIAL today and understand why Mosyle is everything you need to work with Apple.
In a recent web update, Apple made changes to its security releases page to better organize prior years’ security updates and Rapid Security Responses. The company also cleverly included a subtle nod to its Security Bounty Program.
If you’re an IT admin, you’ve got a lot on your plate. Managing the entire user lifecycle can feel like a complex laundry list of manual tasks: switching between systems, provisioning access, configuring and retrieving laptops, resetting passwords, and enforcing security policies.
A security researcher has discovered a phishing attack intended to fool iPhone users into installing what is claimed to be an update to their banking app.
The attack works despite iOS protections because what is actually being ‘installed’ is a progressive web app, which involves no App Store vetting or warnings …
9to5Mac Security Bite is exclusively brought to you by Mosyle, the only Apple Unified Platform.Making Apple devices work-ready and enterprise-safe is all we do. Our unique integrated approach to management and security combines state-of-the-art Apple-specific security solutions for fully automated Hardening & Compliance, Next Generation EDR, AI-powered Zero Trust, and exclusive Privilege Management with the most powerful and modern Apple MDM on the market. The result is a totally automated Apple Unified Platform currently trusted by over 45,000 organizations to make millions of Apple devices work-ready with no effort and at an affordable cost. Request your EXTENDED TRIAL today and understand why Mosyle is everything you need to work with Apple.
You’ve heard it time and time again–cybercrime is on an unpredicted rise. This encompasses everything from malware to online scams to intellectual property theft. And if you’re anything like me, it’s increasingly hard to grasp the exponentially climbing figures (hence the title of this week’s column). If the day ends in y, there’s some sort of data leak or hack in the news.
And it is Sunday, after all…
In today’s Security Bite, I want to again shed light on a recent Statista Market Insights survey that predicts the annual cost of cybercrime globally will reach $10.29 trillion by 2025. For perspective, that’s more than one-third of the United States’ GDP, which sits at $25.44 trillion as of writing.
Security researchers have discovered new macOS malware that’s built to steal your most sensitive data. Dubbed ‘Cthulhu Stealer,’ the malware targets users by impersonating popular apps so it can harvest your system password, iCloud Keychain passwords, cryptocurrency wallets, and more.
In a truly epic security fail, the same data was hosted by a partner company which managed to publish its own passwords, enabling absolutely anyone to access the data …
A vulnerability found in Microsoft apps for macOS allowed hackers to spy on Mac users. Security researchers from Cisco Talos reported in a blog post how the vulnerability could be exploited by attackers and what Microsoft has been doing to fix the exploits.
9to5Mac Security Bite is exclusively brought to you by Mosyle, the only Apple Unified Platform.Making Apple devices work-ready and enterprise-safe is all we do. Our unique integrated approach to management and security combines state-of-the-art Apple-specific security solutions for fully automated Hardening & Compliance, Next Generation EDR, AI-powered Zero Trust, and exclusive Privilege Management with the most powerful and modern Apple MDM on the market. The result is a totally automated Apple Unified Platform currently trusted by over 45,000 organizations to make millions of Apple devices work-ready with no effort and at an affordable cost. Request your EXTENDED TRIAL today and understand why Mosyle is everything you need to work with Apple.
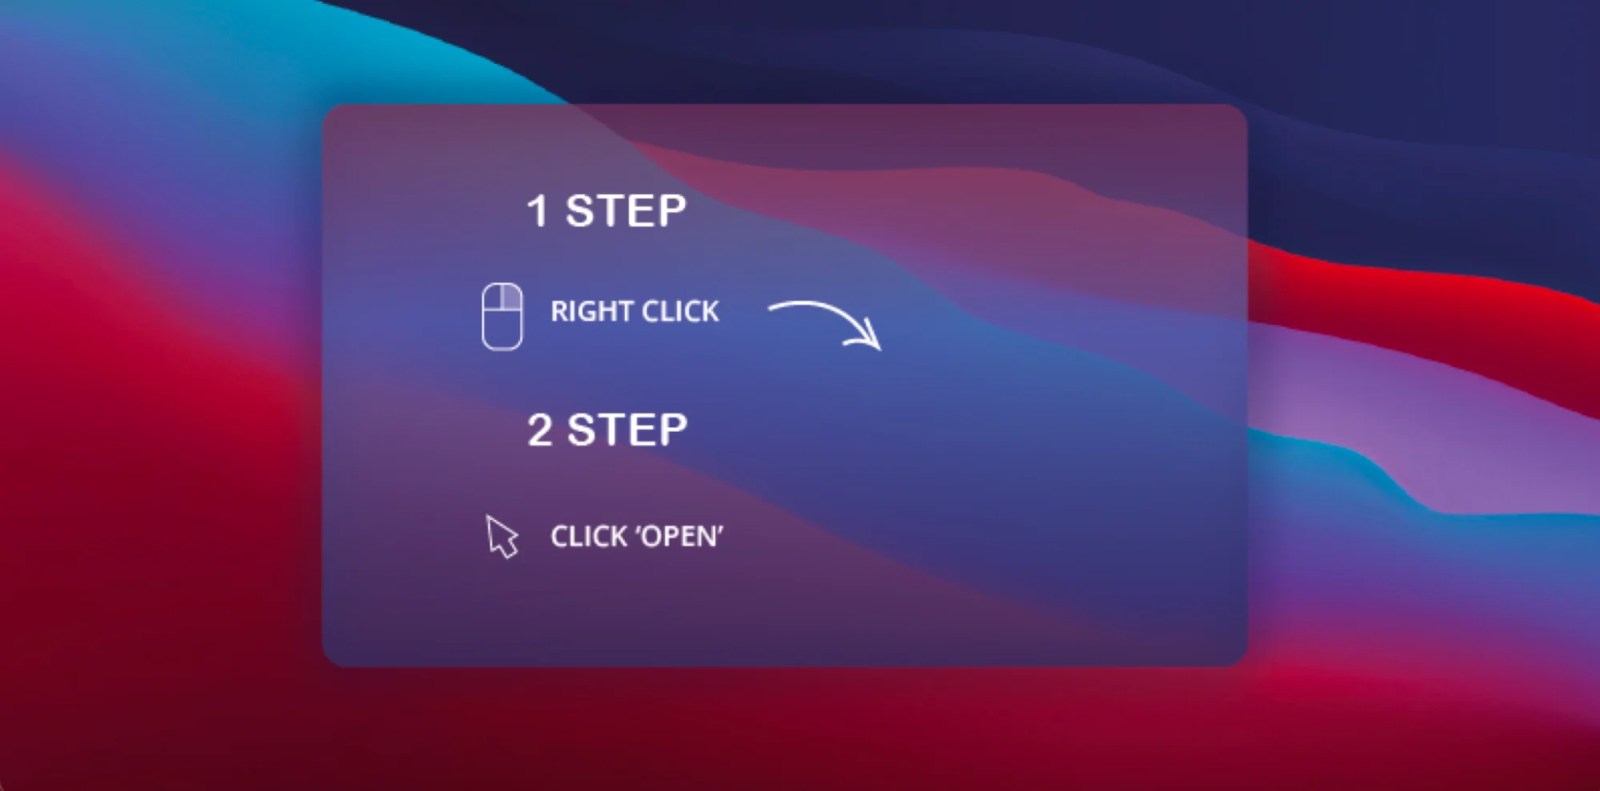
Last week, Apple confirmed that users on macOS Sequoia will no longer be able to Control-click to override Gatekeeper to open software that isn’t signed or notarized by the company. This was a slight change with what I believe will have a significant impact. It also gives us a glimpse into what might happen behind the scenes at Apple as Mac malware gets more clever and the amount of it reach all-time highs.
An Apple ad once made fun of the endless stream of permission requests in Windows Vista, but some are suggesting that Sequoia is now every bit as bad …
1Password has shared that its software for Mac has a vulnerability that exposes users to a potentially serious threat. Along with attackers being able to compromise credentials, the flaw can give bad actors access to your account unlock key.
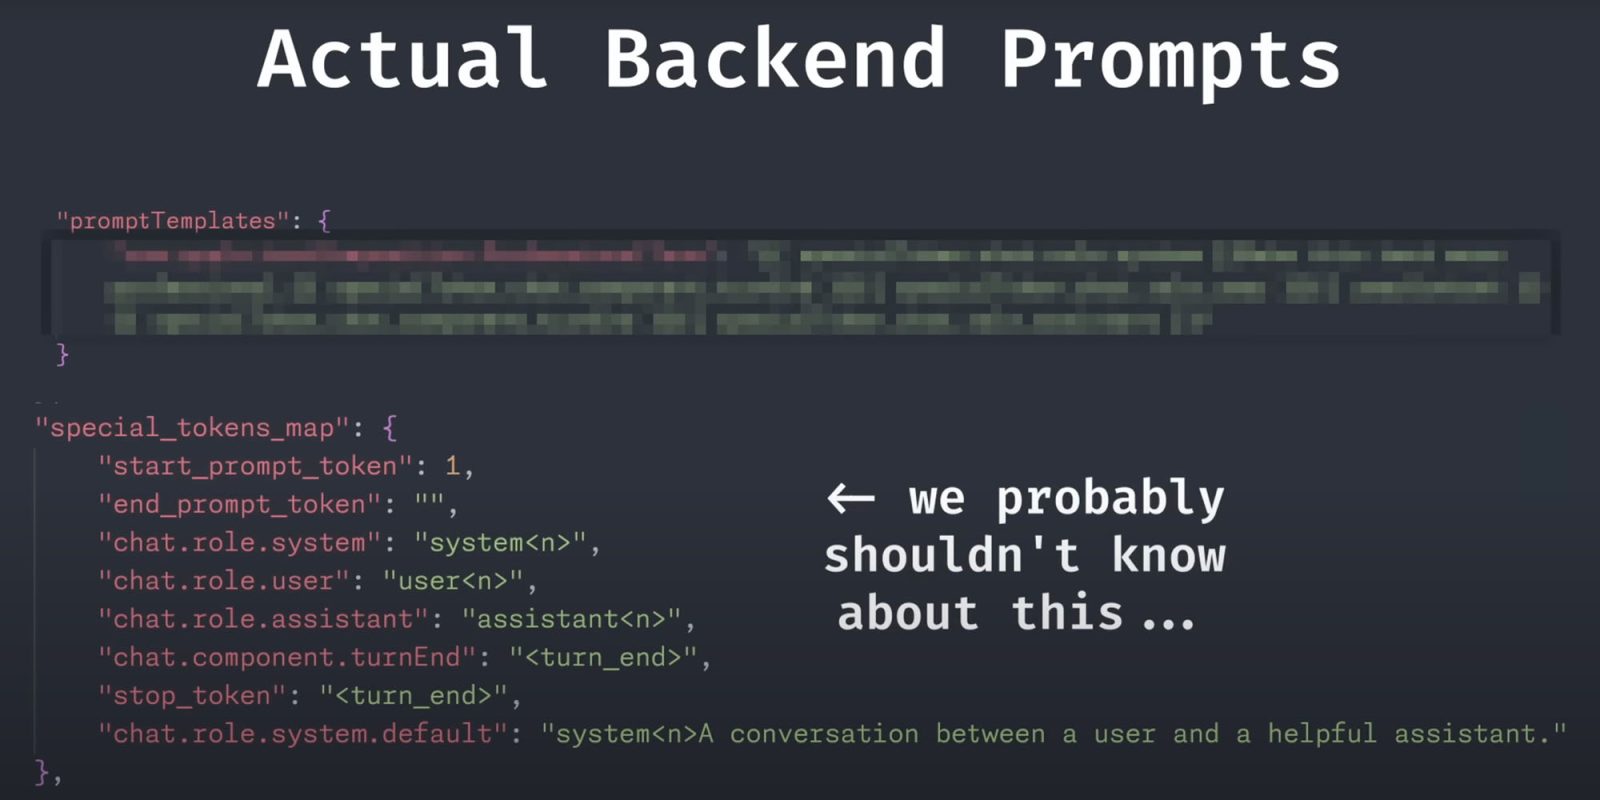
A prompt injection attack on Apple Intelligence reveals that it is fairly well protected from misuse, but the current beta version does have one security flaw which can be exploited.
However, the issue would be very easy for the company to fix, so this will almost certainly be done before the public launch …
Apple and other tech companies are constantly looking for ways to improve the security of their operating systems. Even so, some things go unnoticed. An exploit from 18 years ago is still being actively used by hackers to access internal networks, but Apple has already confirmed that it will fix this with macOS Sequoia.
Apple continually updates and refines its security protections across all its software. In macOS Sequoia, there’s a small change coming that makes it harder to run certain apps. Here’s what you need to know.
9to5Mac Security Bite is exclusively brought to you by Mosyle, the only Apple Unified Platform.Making Apple devices work-ready and enterprise-safe is all we do. Our unique integrated approach to management and security combines state-of-the-art Apple-specific security solutions for fully automated Hardening & Compliance, Next Generation EDR, AI-powered Zero Trust, and exclusive Privilege Management with the most powerful and modern Apple MDM on the market. The result is a totally automated Apple Unified Platform currently trusted by over 45,000 organizations to make millions of Apple devices work-ready with no effort and at an affordable cost. Request your EXTENDED TRIAL today and understand why Mosyle is everything you need to work with Apple.
A leading cybersecurity firm, Picus Security, has released its annual Blue Report study that analyzes the state of exposure management at organizations. The study uses 136 million simulated cyberattack scenarios executed by Picus customers from January to June 2024 to assess the effectiveness of security measures on Windows, Linux, and macOS systems in an organization’s environment.
In this year’s Blue Report 2024, Picus revealed a massive gap in macOS Endpoint Detection and Response (EDR) misconfigurations leading to vulnerabilities.
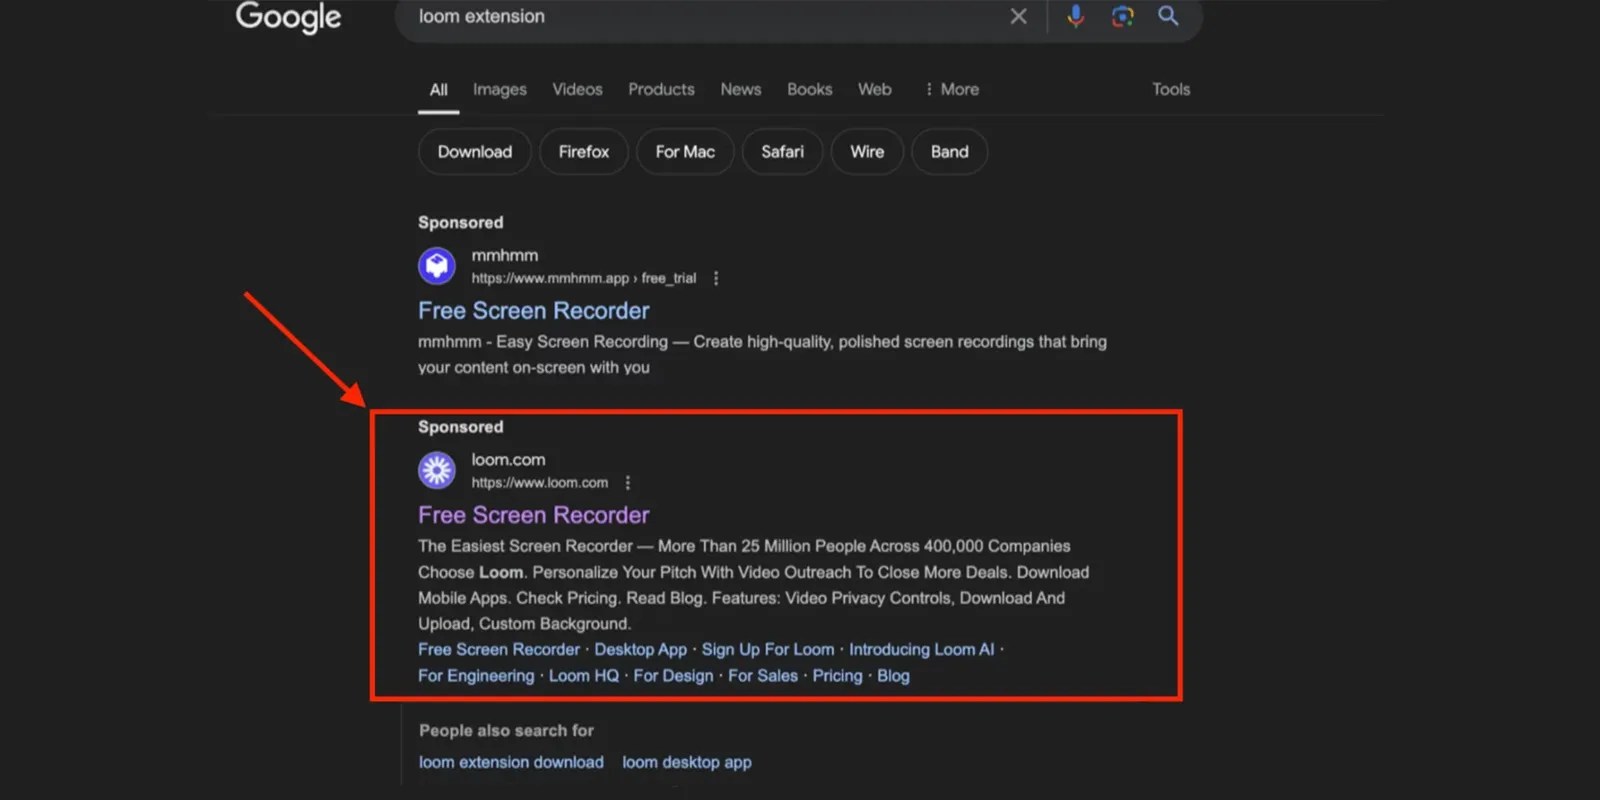
A “sophisticated and alarming” Mac malware attack is being carried out in the guise of free versions of popular apps like the screen recording utility Loom, cryptocurrency manager LedgerLive, and MMO game Black Desert Online.
It appears to be a well-organized attack, with the fake Mac app offers promoted through a combination of legitimate-looking Google ads and phishing emails …
CrowdStrike has nearly run its full course of damage, and Microsoft is looking ahead to prevent the next such catastrophe. Step one in the company’s playbook? Follow Apple’s lead and make Windows security more Mac-like by limiting kernel access.
9to5Mac Security Bite is exclusively brought to you by Mosyle, the only Apple Unified Platform.Making Apple devices work-ready and enterprise-safe is all we do. Our unique integrated approach to management and security combines state-of-the-art Apple-specific security solutions for fully automated Hardening & Compliance, Next Generation EDR, AI-powered Zero Trust, and exclusive Privilege Management with the most powerful and modern Apple MDM on the market. The result is a totally automated Apple Unified Platform currently trusted by over 45,000 organizations to make millions of Apple devices work-ready with no effort and at an affordable cost. Request your EXTENDED TRIAL today and understand why Mosyle is everything you need to work with Apple.
Security researchers have identified an attempt by state-sponsored hackers from North Korea (DPRK) to target Mac users with infostealer malware through a trojanized meeting app.
Once infected, the malware would establish a connection between the Mac and the attacker’s command and control (C2) server to exfiltrate sensitive data like iCloud Keychain credentials. It was also found to quietly install the remote desktop application AnyDesk and keylogging software in the background to take over machines and collect keystrokes.
The CrowdStrike aftermath is seeing IT teams around the world struggle to restore the 8.5 million Windows PCs taken out by the bug. The mess included thousands of flights cancelled, health centers unable to make appointments, retailer payment terminals down, and even some 911 services unavailable.
Macs weren’t affected thanks to protections put in place by Apple, but Microsoft has reportedly claimed that antitrust law means it’s unable to take the same approach …
The sheer scale of the global IT outage caused by a faulty software update has left many wondering how one update to one company’s security software could have such massive impact.
Ironically, the effect of the CrowdStrike flaw has been almost identical to the very thing it’s intended to prevent …
United, Delta, and American Airlines are among the airlines who have been forced to ground flights. Broadcaster Sky News was taken off-air for several hours. Many retailers have been unable to accept payments. In short, it’s chaos out there …
Leaked documents reveal that Cellebrite can’t unlock iPhones running iOS 17.4 and later, at least as of the date of publication (April 2024). The company has confirmed that the documents are genuine.
A statement reveals that the FBI accessed the locked phone of Thomas Matthew Crooks, the shooter at the Trump rally. There were unconfirmed reports that the device was an iPhone, but it was subsequently revealed to be a Samsung device.
The FBI said on Sunday that attempts to access the phone had not been successful, but just one day later stated that it has now succeeded …